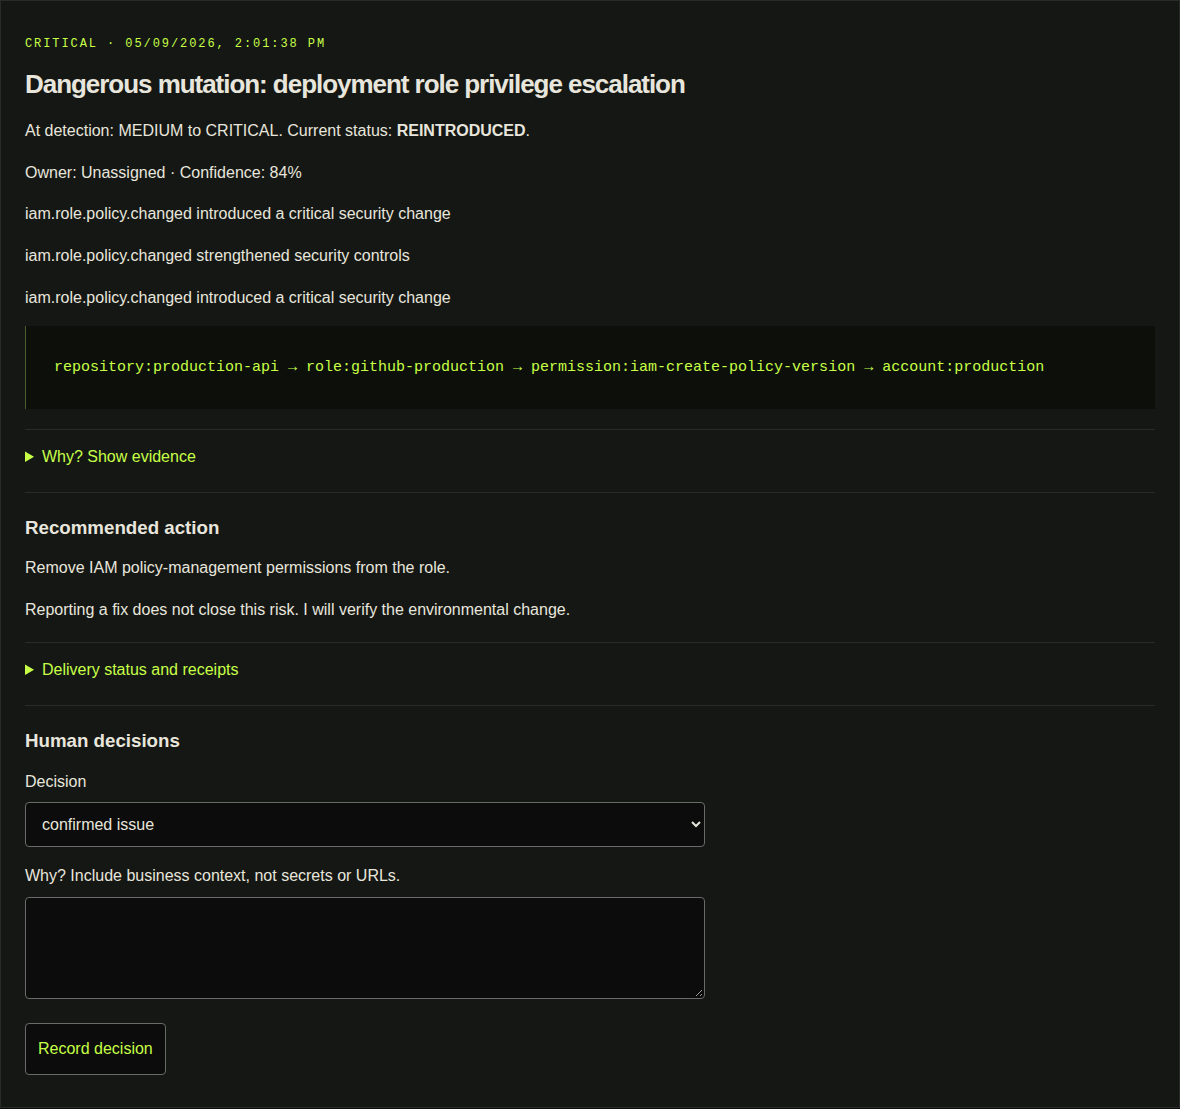
An organism, not another queue.
Security signals only matter when you understand what they mean for this organisation.
The organisation is the context.
An identity, repository, cloud workload, and database are not separate security stories. Their permissions and trust relationships determine what an attacker could reach. blakDNA keeps that connected context in an evolving Security Genome.
The genome includes assets, controls, dependencies, exposure, previous incidents, accepted risks, and the reasons behind human decisions. Its temporal model preserves how those relationships changed, rather than overwriting yesterday's understanding.
Change is not automatically a threat.
Deployments, new applications, and changed permissions are part of a living organisation. blakDNA evaluates a mutation against prior state, organisational patterns, deterministic security knowledge, business context, and reachable attack paths.
Most observations should be absorbed or remembered. Material changes become investigations and evidence-backed calls to action. The goal is less noise without learning to ignore insecurity.
The response is part of the product.
A recommendation has an outcome. Human rationale becomes immune memory; an independent environmental observation confirms whether the risk actually changed. A person reporting a fix is not the same as a verified fix.
The current vertical slice demonstrates this lifecycle with a synthetic GitHub Actions and AWS IAM organisation. Integration coverage and customer deployment readiness should be checked with the team; this site does not imply a universal sensor catalogue or a live Marketplace listing.
From dangerous change to stronger immunity
See the risk.
Prove the recovery.
One new permission. A path into production. Follow how blakDNA explains the danger, remembers the response, verifies the fix, and recognises the pattern next time.
Actual product, synthetic organisation. Illustrative AWS observations and deterministic test reasoning; not customer telemetry or production deployment proof.
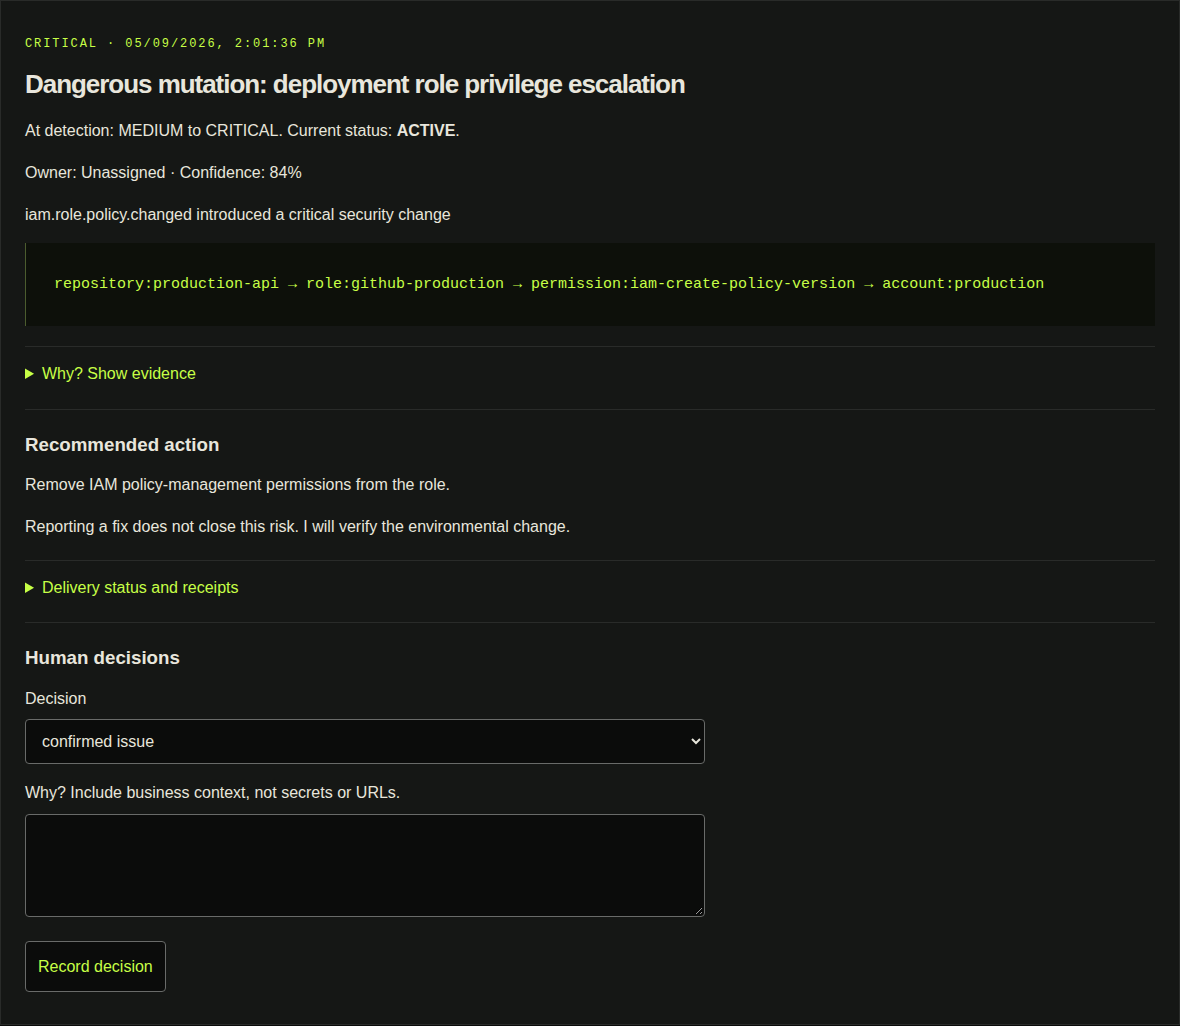
Catch the change that opens a path
A deployment role gains policy-management rights. blakDNA connects the permission to a new privilege-escalation path and calls out what matters.
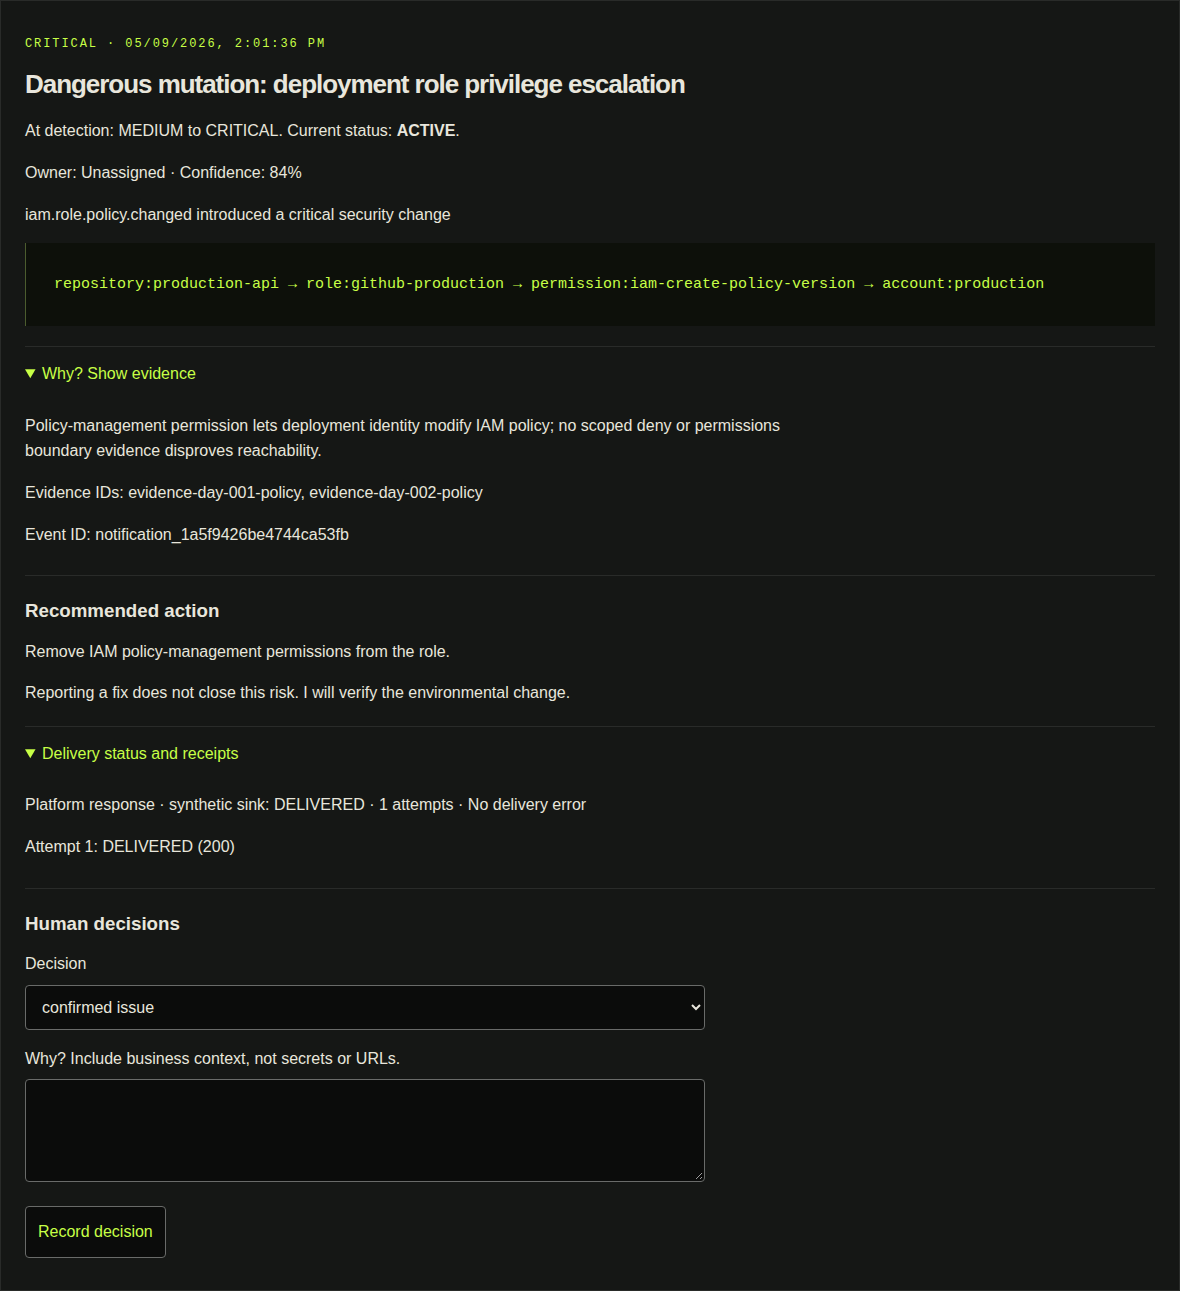
Know why the risk matters
Inspect the attack path, supporting evidence and reasoning summary. Understand what an attacker could reach, not just which setting changed.
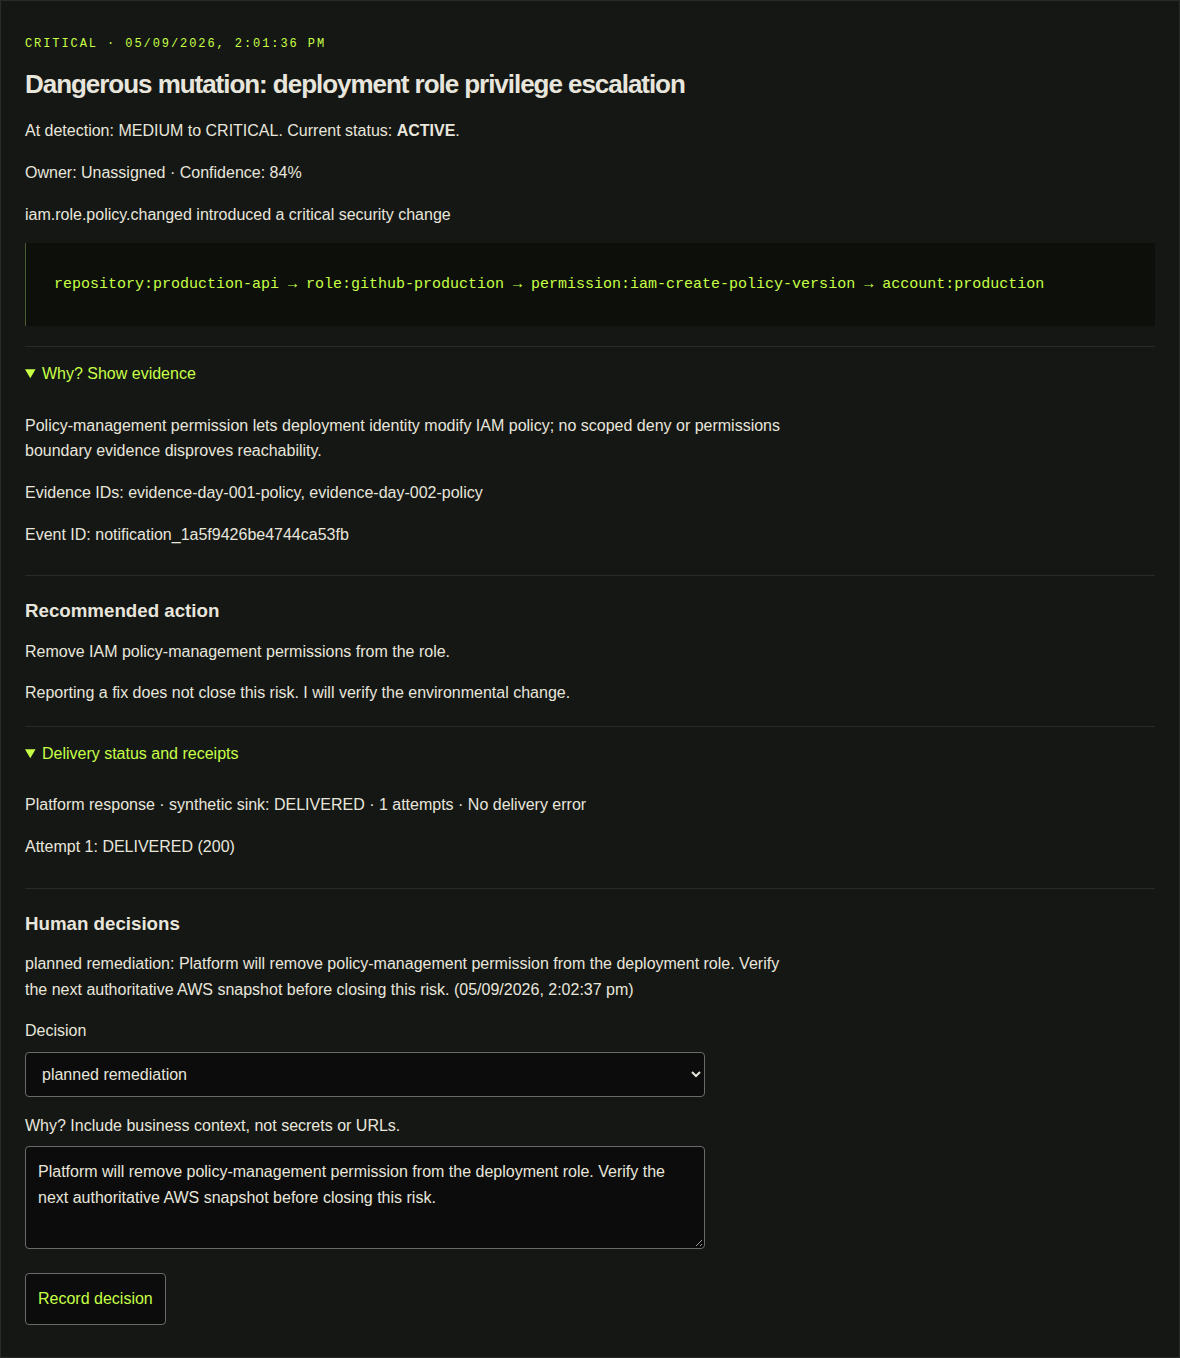
Teach it the reason, not the dismissal
Record business context and a remediation decision. blakDNA remembers the explanation without confusing a human response with a verified fix.
Prove the path is gone
A fresh observation confirms the permission was removed. The attack path disappears, risk becomes mitigated, and the outcome enters immune memory.
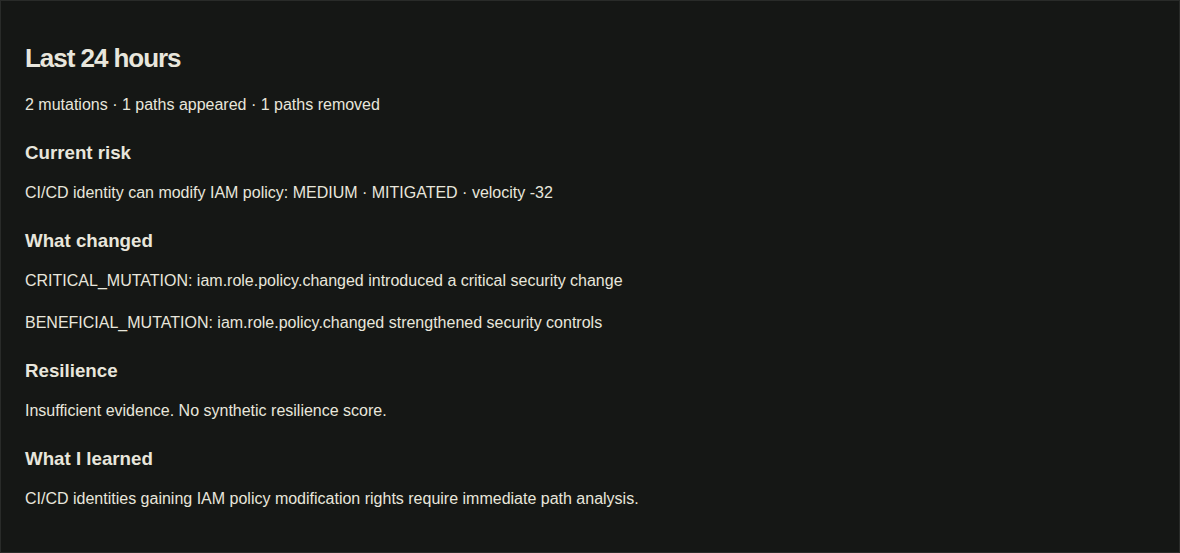
Turn experience into adaptive immunity
An antibody proposal captures the learned pattern. Historical replay and human approval gate activation, so learning never silently rewrites security controls.
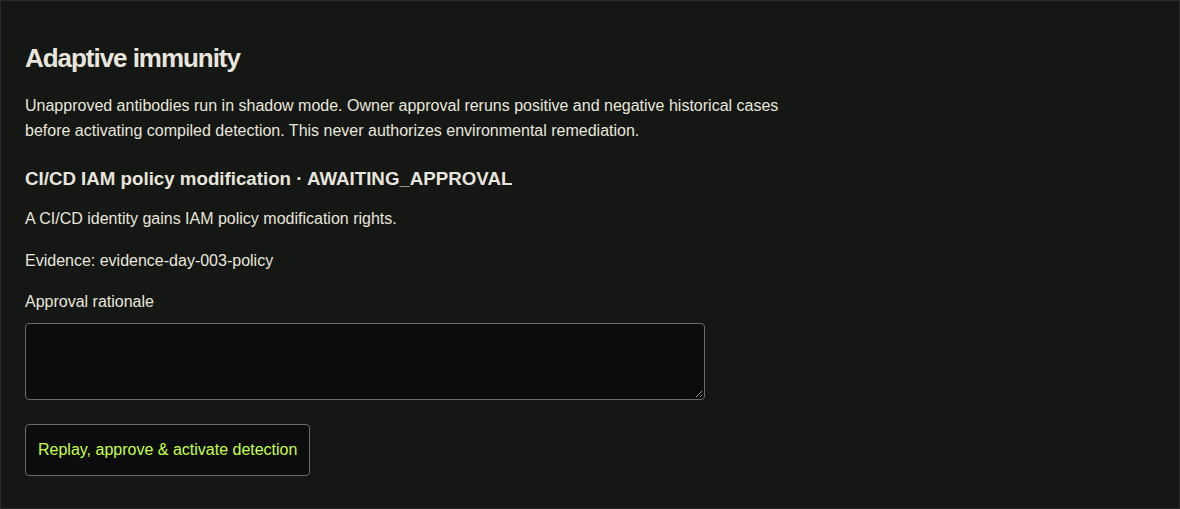
Recognise the weakness when it returns
The same dangerous permission returns. blakDNA identifies reintroduced risk instead of treating yesterday’s resolution as today’s protection.